M&A Data Room Lessons From Deal Delays
Learn how data room design, permissions, Q&A, redaction and disclosure governance can reduce avoidable delays in M&A due diligence.
An M&A data room can reduce avoidable deal delays when it gives reviewers a stable index, approved documents, clear permissions, accountable answers and a usable record of changes. It can also create delays when the room is opened too early, files are duplicated, ownership is unclear or every request requires a manual workaround. The software is only one component. Preparation, decision rights and disclosure governance determine whether the room accelerates review.
This guide does not claim that better document management can prevent every delayed or failed deal. Regulatory review, financing, valuation, third-party consent and commercial findings may legitimately change a timetable. The focus is narrower: operational friction that a sell-side team can identify and control before and during diligence.
The short answer
Most controllable data-room delays arise from six conditions: an unstable folder index, incomplete request ownership, unreviewed files, permission exceptions, fragmented Q&A and late evidence collection. The practical response is to prepare an authoritative document set, assign owners and reviewers, simulate buyer access, release information in planned stages and preserve an audit-ready close record.
Delay pattern 1: opening an incomplete room
Teams sometimes open a room because the launch date has arrived, even though the request list is only partly complete. Reviewers encounter empty folders, placeholder files and conflicting versions. They then create questions to confirm whether information is missing, outdated or intentionally withheld. The seller must answer those questions while continuing to assemble the room, which creates two parallel workstreams and inconsistent expectations.
Figure 1: A focused remediation session can clear document bottlenecks before they delay the next stage of deal review.
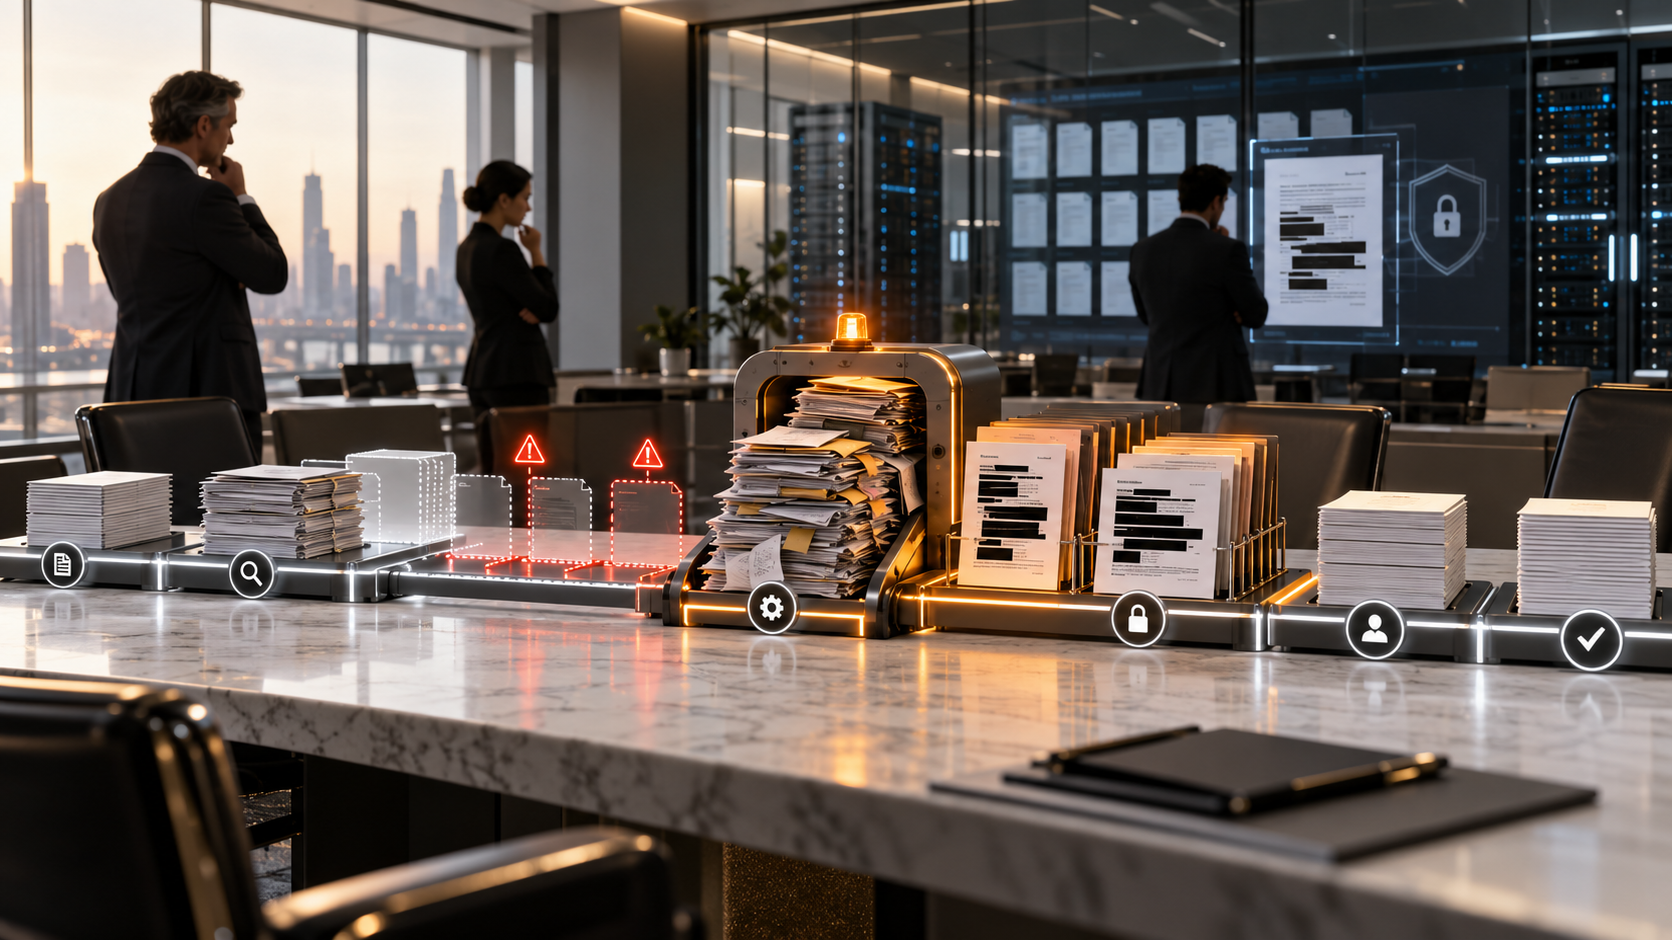
The process map below identifies the primary failure points that introduce friction and extend diligence timelines:
A better readiness standard is based on criticality, not raw completion percentage. Identify the documents that buyers need to validate the investment thesis, financial position, ownership, material contracts, employees, intellectual property, tax and regulatory exposure. For each item, record status, source, owner, internal reviewer, confidentiality class and release stage. Open the room only when the first approved stage is coherent and the missing-item process is explicit.
Do not label a room "complete" merely because every request row contains a file. A duplicated old contract may satisfy a count while providing the wrong evidence. Readiness requires document-level review.
Delay pattern 2: a folder tree that reflects the seller, not the review
Internal drives evolve around departments, personalities and history. A diligence index should instead help outside reviewers answer transaction questions. Copying the internal drive directly can produce abbreviations, unexplained project names, personal working folders and inconsistent date formats.
Start with a standard diligence index, then adapt it to the target, sector and transaction. Use stable numbering so references remain clear even when labels evolve. A practical top level may cover corporate, finance, commercial, material contracts, people, intellectual property, technology and security, tax, regulatory, litigation, insurance and transaction materials.
Keep the hierarchy shallow enough to scan. If a reviewer must open six nested folders to find one agreement, the structure is working against them. Provide an index or request register that maps each request to the released item. Avoid creating separate copies of the same file for several requests; use a cross-reference when the platform permits it.
Delay pattern 3: document versions cannot be trusted
Buyers slow down when several files appear to be the same agreement, model or policy but contain different dates or terms. The review team may compare them manually, raise questions or pause analysis until the seller identifies the authoritative version.
Define a source of truth before upload. Use a naming standard that includes the entity, document type, counterparty or subject, effective date and execution status where relevant. Mark drafts clearly and keep internal working versions outside the published room. When replacing a disclosed file, preserve the prior release history and notify affected reviewers if the change is material.
For executed agreements, confirm signatures, schedules, amendments and side letters. An unsigned master agreement without later amendments may be less useful than a complete contract family. For financial models, identify the model date, reporting period, scenario and approved owner.
Delay pattern 4: redaction becomes a late queue
Redaction work is often underestimated. Sensitive content may include personal data, customer names, pricing, source code, privileged material, clean-team information and information restricted by contract. If classification begins only when a buyer asks for a file, legal and business reviewers become a bottleneck.
Use the following operational readiness checklist to identify and resolve data room bottlenecks before buyers begin review:
Create disclosure classes during preparation. Examples include general buyer access, named bidder only, clean team, external counsel only, summary only and not releasable without consent. Record the reason for each restriction so the team can make consistent decisions. Where a redacted copy is released, retain the approved original internally and maintain a relationship between versions.
Automated redaction may help locate patterns, but it should not be treated as infallible. Test exported files, image layers, comments, hidden sheets, metadata and copy-paste behavior. A black rectangle placed visually over text is not necessarily secure redaction.
Delay pattern 5: permissions are designed after invitations
Permission problems are costly because they interrupt review and can expose confidential information. Common causes include inherited access, users placed in the wrong group, a restricted file uploaded to a general folder or direct invitations that bypass a group model.
Design groups before adding external users. Separate seller administrators, internal contributors, advisers, buyer teams, lenders, clean-team members and specialist reviewers. Map each folder or document class to those groups. Use representative test accounts to confirm what each group can search, preview, download, print and see in notifications.
Test negative cases as deliberately as positive ones. A bidder should not infer another bidder's identity from question lists, user directories or email notifications. A removed user should lose access through every route. An expired link should not remain usable in an old browser session beyond the intended behavior.
Delay pattern 6: Q&A is split across email and spreadsheets
When questions arrive through several channels, teams lose numbering, ownership, approval status and a reliable record of what was disclosed. Duplicate questions consume reviewer time, while inconsistent answers create risk.
Use one controlled Q&A register. Define who may submit, triage, assign, draft, review and publish. Distinguish an internal draft from an externally released answer. Decide when an answer is visible only to the asking party and when an approved response may be shared with all parties. Attach supporting documents through the same controlled release process.
Set service expectations by question category. A routine document pointer may be answered quickly, while tax, employment or regulatory questions require specialist review. Escalate aging questions visibly rather than allowing them to disappear in inboxes.
Delay pattern 7: there is no decision log
Diligence involves repeated decisions: withhold, redact, release, replace, correct, extend access or escalate. If the reasoning remains in personal messages, another administrator cannot reproduce the decision and the closing record is incomplete.
Maintain a concise disclosure decision log containing date, request, decision, approver, reason, affected parties and any follow-up. The log should not become a substitute for legal advice or contain unnecessary privileged analysis. Its role is operational consistency.
Delay pattern 8: analytics are mistaken for intent
Activity data can help the team see whether invitations worked, which documents attract review and where access problems occur. It cannot prove that a bidder agrees with a term, understands a risk or plans to increase an offer. Overinterpreting page views can distract management and produce poorly timed follow-up.
Use analytics as one signal. Combine them with formal questions, meeting feedback and adviser context. Explain internally that view counts may be affected by previews, repeated sessions, shared review responsibilities or technical behavior.
A preventive workflow before launch
Four weeks before opening
- Approve the diligence index and request register.
- Name functional owners and legal reviewers.
- Classify sensitive information and consent dependencies.
- Choose the platform based on group, Q&A, export and archive needs.
- Begin contract-family and financial-model reconciliation.
Two weeks before opening
- Upload the approved first-stage set.
- Check file names, dates, execution status and duplicates.
- Configure groups and default rights.
- Prepare redacted or summarized versions.
- Draft room instructions and a contact route for access problems.
Before invitations
- Test with synthetic buyer, bidder, lender and clean-team accounts.
- Search for unexpectedly visible filenames or snippets.
- Test download, print, copy, notifications and expiry.
- Confirm the Q&A approval route.
- Export a baseline index and permission report.
During diligence
- Hold a short daily room-operations review.
- Track new requests, aging questions and pending approvals.
- Reconcile newly released files with the request register.
- Record material corrections and replacements.
- Review unusual access events without assuming bad intent.
Deal-delay diagnostic table
| Symptom | Likely process cause | Corrective action |
|---|---|---|
| Repeated "is this complete?" questions | Empty folders or unclear request status | Publish a current request register and state what is pending |
| Reviewers cite different contract versions | No authoritative source or replacement protocol | Reconcile the contract family and identify the operative set |
| Access tickets spike after each release | Group model is unclear or untested | Test effective access and simplify permission exceptions |
| Counsel becomes a redaction bottleneck | Sensitivity was classified too late | Triage documents earlier and create disclosure classes |
| Answers conflict across bidders | Q&A is fragmented | Use one approval and publication workflow |
| Closing archive is disputed | Export requirements were not defined | Test archive content and format before signing the contract |
What the platform must support
A transaction room should match the approved operating model. Relevant capabilities may include granular group permissions, numbered indexing, bulk upload, version controls, Q&A, redaction support, watermarks, activity exports and a closing archive. A small process may not need every enterprise feature. A large auction should not rely on a lightweight tool merely because it is familiar.
For a small approved package rather than a full auction, a controlled document service such as SendNow secure file sharing can be evaluated for recipient verification, expiry, revocation and engagement records. It should not be represented as a substitute for formal bidder separation, structured Q&A or clean-team administration unless the tested configuration supports those requirements.
Related resources include the M&A data room checklist, M&A virtual data room workflow and buy-side versus sell-side data room guide.
Closing the room without creating a new delay
Define closure at the beginning. Identify who authorizes the final export, which versions belong in the record, how Q&A and activity are preserved, whether the archive requires special software and when external access ends. Ask for a sample archive during procurement and test it outside the live platform.
Reconcile the final index with the request register and disclosure log. Record unresolved items, later deliveries and material corrections. Remove external users and temporary administrators according to the approved schedule. Retain or delete the room under the organization's legal, privacy and records obligations.
Frequently Asked Questions
Can a VDR prevent an M&A deal from being delayed?
No. It can reduce document and access friction, but commercial, regulatory, financing and diligence findings can still change the timetable.
When should a sell-side data room be opened?
Open it when the first approved disclosure stage is coherent, critical documents are reviewed, permissions are tested and pending items are visible in a controlled request process.
What causes the most data-room questions?
Missing items, unclear versions, incomplete agreement families, unexplained financial data, inconsistent naming and uncertain disclosure status commonly generate avoidable questions.
Should every buyer receive the same documents?
Not necessarily. Access may vary by stage, bidder, jurisdiction, clean-team rule or confidentiality need. Differences should follow an approved, documented model.
How often should permissions be reviewed?
Review them before launch, after material group changes, before sensitive releases and periodically during the process. Test effective access with representative accounts.
Is page-view data reliable evidence of bidder interest?
It is evidence of recorded platform activity, not proof of interest or understanding. Use it carefully with other transaction signals.
What should be included in a closing archive?
The required set may include final files, index, users, permissions, Q&A, activity, release history and administrative records. Define the scope with legal and records advisers.
Sources and verification notes
- Federal Trade Commission: Protecting Personal Information
- NIST SP 800-53 Rev. 5: Security and Privacy Controls
- NIST SP 800-92: Guide to Computer Security Log Management
- UK Information Commissioner's Office: Data protection by design and default
This article provides operational education, not legal, tax, investment or cybersecurity advice. Sources were reviewed on October 3, 2026.